Fixes are available in PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Versions 8.1 and older are end-of-life and receive no official upstream patches.
| PHP Branch | Vulnerable Versions | Patched Version |
| PHP 8.5 | Before 8.5.12 | 8.5.12 |
| PHP 8.4 | Before 8.4.27 | 8.4.27 |
| PHP 8.3 | Before 8.3.36 | 8.3.36 |
| PHP 8.2 | Before 8.2.35 | 8.2.35 |
| PHP 8.1 and older | All versions (End-of-Life) | None (requires vendor backports or upgrade) |
Key Details
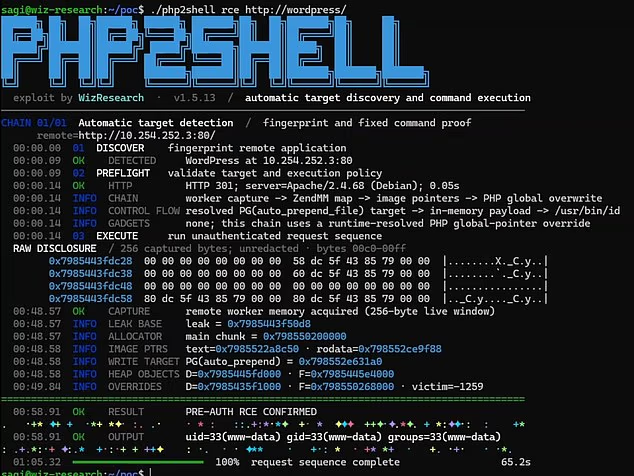
The Vulnerabilities: Tracked as CVE-2026-109618 and CVE-2026-109619, these core memory-safety issues allow unauthenticated remote code execution (CVSS 9.2).
Attack Vector: They can trigger during request handling or out-of-memory error cleanup before your application code even runs, affecting runtimes like Apache mod_php, PHP-FPM, php-cgi, and LiteSpeed.
Official Guidance: Review the full advisory details on the PHP.net Security Advisories page
Patching
Upgrading PHP is the only complete remediation. The measures below may reduce exposure to specific exploitation paths while you prepare to upgrade, but they do not address every variant.
- Set
expose_php = Off - Set
memory_limitto the maximum size you need for your application. - Lower
post_max_sizeto a value compatible with your application's upload requirements. - Set
display_errors = 0in production to prevent PHP error output from being exposed to remote users.
Some measures can affect application functionality, performance or availability. Test configuration changes against your application's requirements and apply the PHP security update as soon as possible.
It shouldn't do any harm to add the following code to your .htaccess file... (XCMS already uses this code)
# Disable Apache Server Signature
ServerSignature Off

# Hide PHP Version
<IfModule mod_headers.c>
  Header unset X-Powered-By
  Header always set X-Content-Type-Options "nosniff"
</IfModule>

# Protect Against PHP Fingerprinting Attacks
<IfModule mod_rewrite.c>
  RewriteCond %{QUERY_STRING} PHP[a-z0-9]{8}-[a-z0-9]{4}-[a-z0-9]{4}-[a-z0-9]{4}-[a-z0-9]{12} [NC,OR]
  RewriteCond %{REQUEST_URI} =PHP[a-z0-9]{8}-[a-z0-9]{4}-[a-z0-9]{4}-[a-z0-9]{4}-[a-z0-9]{12} [NC]
  RewriteRule .* - [F,L]
</IfModule>